




Electromechanical integration services should be defined by the behavior of the complete system, not simply by a list of supplied components. A motor can meet its specification, a control panel can pass inspection, and a mechanical assembly can match its drawing while the combined machine still fails to start reliably, achieve output, or stop safely. The scope must therefore connect component responsibilities to interface ownership and measurable system-level acceptance criteria.
The decisive step is to agree on verification before design and purchasing commitments become difficult to change. Factory acceptance testing establishes what the assembled system can demonstrate before shipment; site acceptance testing establishes what it can demonstrate after installation under agreed operating conditions. Neither should depend on an undefined promise that the equipment will be “fully operational.”
Define the operating boundary before the supply boundary
A scope described as “mechanical assembly, electrical installation, and commissioning” leaves important questions unanswered. Does commissioning include production trials? Who provides representative materials? Does electrical installation stop at the cabinet terminals, or include field cables, protective bonding, and upstream power connections? Who resolves a positioning error caused by the interaction between mechanical backlash and control tuning?
Begin with the intended operating envelope: loads, speeds, duty cycles, environmental conditions, utility requirements, operating modes, and interfaces with adjacent equipment. Distinguish guaranteed conditions from design assumptions. A conveyor specified for a defined product mass and spacing cannot reasonably be accepted against an unspecified mix of products.
The physical boundary should identify connection points rather than broad equipment labels. Examples include the incoming supply terminals, compressed-air isolation valve, mounting datum, upstream transfer point, and network connection to the plant system. Each boundary needs a corresponding functional definition: what passes across it, under what conditions, and which party provides or verifies it.
Useful scope deliverables include:
- Mechanical layouts, mounting requirements, tolerances, and access provisions.
- Electrical schematics, load information, cable schedules, and protective bonding arrangements.
- Control architecture, operating sequences, alarm behavior, and an agreed input/output list.
- Interface definitions for utilities, adjacent machines, and external software systems.
- Installation, commissioning, verification, training, and handover obligations.
Exclusions require equal precision. If foundations, incoming power, network infrastructure, or production materials are outside the integration contract, specify their required characteristics, delivery dates, and verification responsibility. An excluded item can still be a critical dependency; exclusion does not remove its effect on system acceptance.
Give every interface a technical owner
A responsibility matrix is useful only when it identifies who makes the technical decision at a boundary. Separating “mechanical” and “electrical” responsibilities is insufficient where a drive, coupling, gearbox, encoder, and motion controller jointly determine positioning performance.
An interface register should record both the provider and the receiver, the agreed parameters, the evidence required, and the person authorized to approve changes. Assign a coordinating owner for cross-disciplinary issues so that unresolved assumptions do not become installation decisions.
Software interfaces need more than a protocol name. Define data meaning, units, update rates, timeout behavior, command authority, and the response to stale or invalid information. Two devices can communicate successfully while interpreting the same message differently.
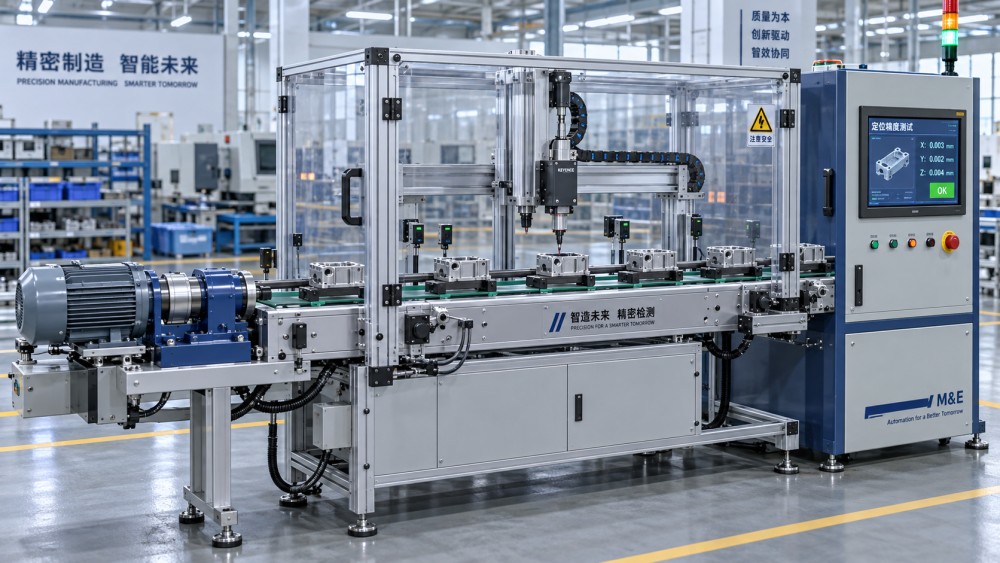
Convert requirements into testable acceptance statements
Acceptance criteria should describe an observable outcome, the conditions under which it must occur, and the method used to determine compliance. “Smooth operation,” “adequate accuracy,” and “stable production” do not provide a defensible basis for acceptance.
For a positioning axis, define the measurement datum, load, travel range, approach direction, tolerance, and measurement method. For a handling system, define representative products, feed conditions, acceptable damage, and transfer behavior. For throughput, state whether the measure is cycle rate, gross output, or conforming output over a defined observation period.
Every acceptance-critical requirement should have a unique identifier linked to a test, inspection, calculation, or document review. This traceability exposes requirements that cannot yet be verified and tests that do not demonstrate a contractual obligation.
A test specification needs enough detail to be repeatable:
- Approved equipment configuration and software version.
- Prerequisites, utility conditions, test materials, and loading.
- Test procedure, duration or repetitions, and measurement locations.
- Pass/fail limits, measurement equipment, and relevant uncertainty.
- Required records, witnesses, and treatment of deviations.
A numerical tolerance is incomplete without considering measurement capability. If the measurement uncertainty is significant relative to the allowed tolerance, the parties need an agreed decision rule. Otherwise, the same result may support conflicting acceptance judgments.
Acceptance limits should also distinguish individual-cycle performance from sustained operation. A short demonstration can establish sequence correctness but may not reveal thermal drift, accumulated positioning error, or material buildup. Test duration should follow the failure mechanisms and duty cycle being evaluated, not merely the time available for witnessing.
Separate factory evidence from site-dependent evidence
Factory acceptance testing, or FAT, should verify as much of the integrated system as the factory configuration permits. This can include assembly inspection, electrical checks, control sequences, alarm responses, recipe handling, and performance with representative loads. It should also identify which interfaces are simulated and which remain unverified.
Simulation is useful for checking logic, but it has boundaries. A simulated upstream “ready” signal cannot establish that a physical transfer works. A drive running without its production load cannot prove torque margin or loaded stopping behavior. The FAT report should make these distinctions explicit rather than treating all successful demonstrations as equivalent.
Site acceptance testing, or SAT, addresses the installed configuration: foundations, alignment after transport, final cabling, site utilities, adjacent equipment, and actual production conditions. It should repeat tests whose results could be affected by shipment, reassembly, parameter changes, or site integration.
Shipment release, installation completion, permission to energize, permission to begin trials, and final acceptance are separate decisions. Define the evidence needed for each. A successful FAT may authorize shipment without authorizing unrestricted production operation after installation.
A site-readiness review should precede mobilization. Confirm utility availability, access, lifting arrangements, installation prerequisites, representative materials, and attendance by parties needed for interface testing. If these conditions are unavailable, the contract should distinguish an integration defect from a blocked test and define how rescheduling is handled.
Test safety functions and failure recovery, not just normal operation
A machine that completes its normal sequence has not necessarily demonstrated safe behavior. Safety verification must follow the risk assessment, the implemented protective measures, and the requirements applicable to the equipment and destination market. The contract should identify responsibility for risk assessment, safety-related design, validation, and required conformity documentation.
Standards such as IEC 60204-1 for machine electrical equipment, ISO 13849-1 for safety-related control-system design, and ISO 13849-2 for validation may be relevant, depending on the application. Referencing a standard does not by itself establish compliance; the applicable edition, scope, and required evidence must be determined for the project.
Test cases should address emergency stops, guard interlocks, loss and restoration of power, communication failures, and other faults identified by the risk assessment. Check the complete response: hazardous motion, stored energy, fault indication, reset conditions, and restart authorization. An emergency stop need not remove all energy indiscriminately; the required response must achieve the defined safe condition.
Reset and restart deserve separate checks. Clearing a fault or closing a guard should not inadvertently initiate hazardous motion. Where stopping time determines protective-device positioning, it must be assessed under the relevant worst-case conditions, not only with an unloaded mechanism.
Fault testing should be planned and controlled. Use approved simulation or injection methods where appropriate, with competent personnel and suitable precautions. Improvised fault creation can damage equipment or expose people to hazards without producing reliable validation evidence.
Make performance tests representative without making them open-ended
Performance disputes arise when the test material or operating conditions differ from the design basis. A feeding mechanism may behave differently with changes in friction, dimensional variation, rigidity, or surface condition. A pump system depends on the installed hydraulic conditions. A motion system can meet its target with one load but not another.
Define a bounded test matrix covering the important operating extremes and representative normal conditions. Selection should follow technical sensitivity: maximum load, minimum product size, challenging transfer geometry, or the duty cycle most likely to expose heating. Testing every possible combination may be impractical, but testing only the easiest combination provides weak evidence.
For sustained-output tests, agree how downtime and rejected output are counted. Distinguish equipment faults from unavailable feed material, upstream stoppages, and operator interventions, while retaining an unedited event record. Excluding interruptions without an agreed rule can turn an apparent performance result into a contractual dispute.
Record configuration changes during testing. Drive parameters, control timers, mechanical adjustments, and software revisions can invalidate earlier results. A successful test should be tied to the delivered baseline, with targeted regression testing after changes that could affect previously verified functions.
Close deviations with evidence and preserve the accepted baseline
The acceptance process needs a defined route for incomplete or failed items. Classify deviations by their effect on safety, mandatory obligations, functionality, performance, and maintainability. Unresolved safety-critical items should block authorization for the affected operation. Minor documentation defects may permit conditional acceptance if their consequences and closure obligations are explicit.
A punch list should identify the requirement, observed condition, corrective action, owner, deadline, and retest evidence. “To be resolved during warranty” is not an adequate substitute for an unmet acceptance requirement. Warranty addresses obligations after delivery; acceptance establishes whether the agreed delivery has been achieved.
Change control must remain active during commissioning. Record why each change is needed, who approves it, and its effect on cost, schedule, safety, interfaces, documentation, and testing. Adjustments that improve one subsystem can create new loads, timing conflicts, or stopping behavior elsewhere.
Final handover should preserve the accepted configuration through as-built drawings, software and parameter backups, restoration instructions, maintenance requirements, test records, and access credentials handled through an appropriate security process. Confirm any licensing or access restrictions that could prevent later maintenance.
The final acceptance record should state the configuration accepted, the conditions tested, any agreed limitations, and any remaining obligations. That makes acceptance a usable engineering baseline—not merely a signature indicating that the equipment ran on the day of inspection.
Related News
- 00
0000-00
How to prevent delamination in laminated flexible packaging films - 00
0000-00
Fujifilm and ePac Partner Globally on Jet Press FP790 Deployment - 00
0000-00
Choosing technical ceramics for wear resistance under impact loads - 00
0000-00
Which compliance standards apply to children's stationery in the US? - 00
0000-00
How to assess a furniture components supplier’s production capacity
Weekly Insights
Stay ahead with our curated technology reports delivered every Monday.